Managers & supervisors
Understand the environmental responsibilities increasingly built into operational roles.
Gain practical, regulated knowledge to help identify, manage and improve environmental performance across your organisation.
Designed for managers, supervisors and developing professionals who need a clear understanding of organisational environmental management.
Understand the environmental responsibilities increasingly built into operational roles.
Broaden your remit where environmental management overlaps with compliance and risk.
Build awareness of impacts, controls, legislation, monitoring and improvement.
Create a regulated foundation before moving into higher-level sustainability roles.
The ProQual unit contains eight major learning outcomes. SHEC Learning® presents them as eight clear learning modules.
60-question multiple-choice examination
90 minutes available
Pass / fail result
This is SHEC Learning®’s current approved-centre delivery arrangement.
ProQual describes internally assessed evidence across the qualification, with external quality assurance. Permitted methods include assignments, projects, reports, worksheets, portfolio evidence and questioning.
Progression should reflect your experience, responsibilities and career direction—not simply follow the next number.
Core environmental-management knowledge for emerging responsibility.
For experienced practitioners with broader sustainability responsibility.
Explore Level 6 →For senior leaders shaping environmental strategy and organisational performance.
Explore Level 7 →A regulated Level 3 qualification providing foundation knowledge in organisational environmental management.
603/6603/5.
There is one mandatory ProQual unit. Its eight major learning outcomes are structured by SHEC as eight learning modules.
30 Total Qualification Time hours, including 20 Guided Learning Hours.
ProQual specifies no formal entry requirements.
No. It is a foundation knowledge Award and does not by itself demonstrate occupational competence.
SHEC Learning® delivers the course entirely through e-learning, with six months of course access.
The current SHEC Learning® offer uses a 60-question multiple-choice examination with 90 minutes available.
It introduces relevant environmental-management-system and ISO-standard concepts. It does not make you an ISO 14001-certified auditor.
Yes, particularly where environmental responsibility is becoming part of the role. As an entry-level e-learning course, no suitability assessment is required.
Enrol online or speak with SHEC Learning® about your environmental career pathway.

All blogs
Preventive Measures
2025-07-08 15:09:10.506508+00
Author Nigel Lewis BA (Hons) CMIOSH OSHCR PIEMA
In the digital world, where cyber threats are increasingly sophisticated, safeguarding your organisation from potential breaches is paramount. Effective cybersecurity goes beyond reactive measures; it necessitates a proactive approach. Implementing robust preventive measures can significantly mitigate risks and fortify your organisation's defences against evolving cyber threats. Proactive cybersecurity ensures that your organisation is prepared to respond and actively defend against emerging risks before they can cause damage.
I strongly believe in the critical importance of proactive cybersecurity measures. With the frequency and sophistication of cyber-attacks increasing exponentially, organizations can no longer afford to rely solely on reactive strategies. Learning and adhering to regulatory standards is crucial, as it ensures that your cybersecurity practices meet legal requirements and help prevent costly breaches. By staying informed about these standards, you can better protect your business from potential threats and demonstrate your commitment to maintaining robust security practices.
The first step in preventing cyber threats is identifying potential vulnerabilities within your organisation. Regular risk assessments help understand the current threat landscape and evaluate existing security measures' effectiveness. The General Data Protection Regulation (GDPR) sets stringent standards for handling personal data, requiring organisations to implement robust security measures. These assessments should be conducted periodically and whenever significant changes occur in your IT infrastructure.
Access control is critical in ensuring that only authorised personnel access sensitive information, serving as one of the key preventive measures for cyber attacks. Implement multi-factor authentication (MFA) and ensure user access is granted based on the principle of least privilege. Regularly review and update access permissions to reflect changes in roles and responsibilities.
Keeping your software, including operating systems and applications, up-to-date is vital in protecting against known vulnerabilities. Regular updates and patches from software vendors often include fixes for security flaws that cybercriminals could exploit. Establish a routine for applying these updates to minimise the risk of an attack.
Employees are often the first line of defence against cyber threats. Regular training and awareness programmes are essential in helping staff recognise and respond to potential threats, such as phishing emails and social engineering attacks. Encourage a culture of vigilance and ensure that employees are familiar with the organisation's cybersecurity policies and procedures.
Develop and enforce comprehensive cybersecurity policies that outline the protocols for handling data, managing access, and responding to security incidents. These policies should be regularly reviewed and updated to address emerging threats. Make sure that all employees are aware of and adhere to these policies.
Investing in advanced security tools can provide an additional layer of protection. Tools such as firewalls, intrusion detection systems, and anti-malware software can help detect and prevent cyber threats. Regularly review and upgrade these tools to ensure they remain effective against evolving threats.
Regularly backing up critical data is essential for ensuring that you can quickly recover during a cyber incident. Implement a robust backup strategy that includes regular, automated backups and secure storage of backup data. Test your backup and recovery processes periodically to ensure they work as expected.
Despite best efforts, cyber incidents can still occur. A well-defined incident response plan can help minimise damage and ensure a swift recovery. Your plan should include procedures for identifying, containing, and mitigating incidents, communication protocols and recovery strategies.
I believe cybersecurity should be at the forefront of every organisationâs strategic priorities. The dynamic nature of cyber threats necessitates an unwavering commitment to preventive measures. Adopting a proactive stance protects your organisation from potential breaches and fosters a culture of resilience and preparedness. Prioritising cybersecurity enables businesses to navigate risks confidently, ensuring long-term stability and protecting their assets and reputation in an increasingly digital world.
Nigel Lewis BA (Hons) CMIOSH OSHCR PIEMA


 Advice
Asbestos in Construction: What Senior Professionals Must Know
Advice
Manual Handling in Construction: Responsibilities at Every Level
Advice
Risk Assessments and Method Statements: Getting RAMS Right
Advice
Work at Height in Construction: Managing the Risk
Driving Culture and Performance in HS
Education and Training
Strategic Environmental Management – A Key Requirement at Level 7
Near Miss Reporting in Construction
The Competent Person in Construction: More Than a Certificate
How to Prepare for a HSE Construction Site Inspection
Advice
Understanding CDM 2015: A Practical Guide
2024-06-12 16:20:00Advice
Construction Site Inspections: Why They Matter and What to Expect
Education and Training
How to Apply for a CSCS Card: A Step-by-Step Guide for UK Construction
Education and Training
Does a Leisure Facility Require a Health and Safety Certificate?
Education and Training
Successful Health and Safety Case Studies in the UK Leisure Industry
Education and Training
Training for Health and Safety in Leisure
Education and Training
Health and Safety Training Programs in the Leisure Industry
Preventive Measures
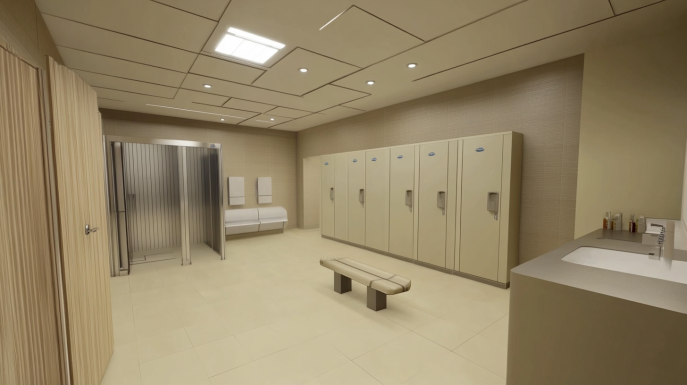
Case Studies on Health and Safety Success in Leisure
Preventive Measures
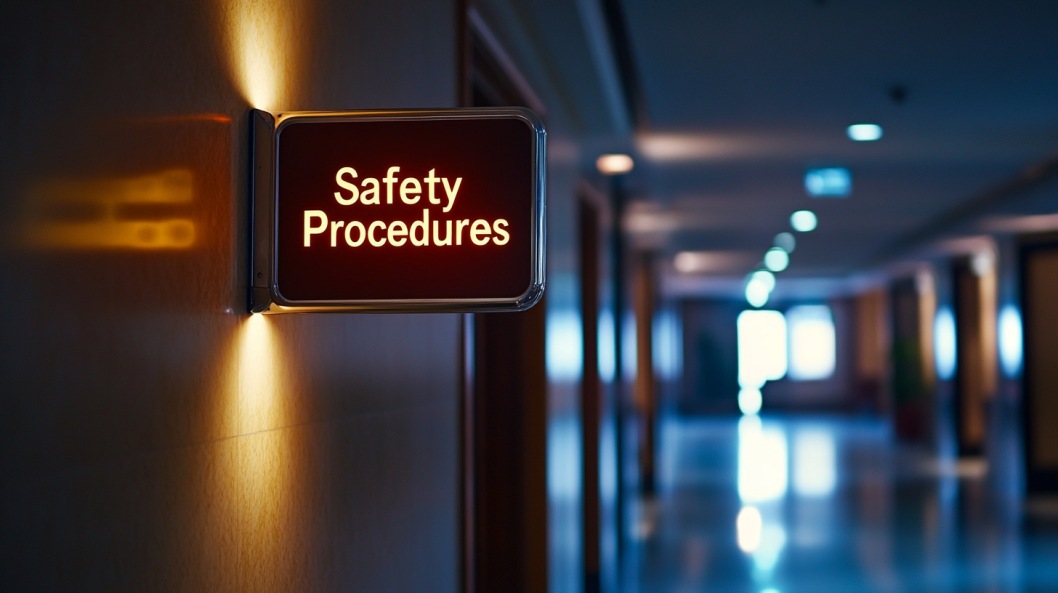
Health and Safety in Leisure Centre Changing Rooms
Workplace Culture
Health and Safety Procedures in Hotels
Workplace Culture
Health and Safety in a Leisure Centre
Becoming a fire risk assessor requires more than learning how to complete a form. Professional competence develops through fire-safety knowledge, appropriate qualifications, practical experience, professional judgement, accurate reporting, continuing professional development and working within the limits of your competence.
There is no single route for everyone. Your right starting point depends on what you can already demonstrate.
Your existing knowledge and experience determine where development should begin. General Health & Safety experience is valuable, but it does not automatically prove occupational fire-risk-assessment competence.
Build a Foundation-level understanding before progressing into supervised assessment activity and real building experience.
Use transferable risk skills while developing specific fire-safety knowledge, building understanding and practical FRA experience.
Develop specialist competence around the premises, occupants, management systems and fire precautions you work with.
Map current evidence against modern competence expectations, identify genuine gaps and progress at the appropriate level.
Foundation development for people building specific fire-risk-assessment knowledge.
Intermediate development with substantially more practical competence and professional reporting.
The government has committed to introducing mandatory independent certification for fire risk assessors in England. The consultation closed on 18 June 2026. As of September 2026, the final framework and implementation arrangements have not yet been brought into force.
This means fire risk assessment is not currently a regulated profession with mandatory certification, although assessors must still be competent for the work they undertake and duty holders must ensure assessments are suitable and sufficient.
This section should be reviewed when government proposals or legislation change.
Structured learning and assessment against defined outcomes, awarded by a regulated awarding organisation.
Independent verification of competence against the rules and standards of a certification scheme.
Recognition through a professional register or body, normally subject to competence, conduct and CPD requirements.
Completing a SHEC qualification does not automatically provide certification, professional registration or unrestricted competence.
✓ Observe experienced and competent assessors.
✓ Begin with simpler, lower-risk premises.
✓ Complete supervised assessment activity.
✓ Receive feedback on findings and reports.
✓ Build evidence across different premises and scenarios.
✓ Develop knowledge of construction and fire protection.
✓ Increase complexity gradually.
✓ Refer work beyond your competence to specialists.
No single degree route is required. You need relevant knowledge, training, experience and other qualities appropriate to the work you undertake.
Yes, but general H&S experience alone is not enough. You must develop fire-specific knowledge and supervised practical experience.
Yes. Facilities and property experience can be a strong starting point, provided fire-specific competence is developed and evidenced.
Potentially. Current ProQual entry permits the Level 3 Award or at least three years’ proven occupational fire-risk-assessment experience, subject to suitability assessment.
Knowledge can be developed online, but professional competence also requires practical experience, assessment activity and evidence that cannot be replaced by online study alone.
There is no universal timescale. It depends on your starting knowledge, access to practical experience, qualification route and the scope of work you intend to undertake.
It is a framework describing competence for individual fire risk assessors at Foundation, Intermediate and Advanced levels. It is not itself a qualification or a step-by-step assessment method.
No. Competence must always be matched to the premises, risks and complexity of the assessment.
Tell SHEC about your background, experience and intended role. We will help you identify the development route that matches what you can already demonstrate.